NorthLight is written by Geordie’s researchers, engineers and product specialists. Our aim is to light the way for security, IT and AI teams navigating the new waters of secure agentic operations.
You'll find real accounts of what we see in customer environments, key product releases, and practical guidance for leading and operationalizing teams.
Two strands with their own rhythm and their own look. They sit alongside the topics rather than replacing them, so an incident analysis about a runtime problem also appears under Runtime.
FIELD NOTESSEEN IN THE FIELD
Incident Analysis
Short accounts of what we have seen in real customer environments.
002 · Large consumer marketplaceA supply-chain incident made an AI coding blind spot visible
001 · Financial services and investment firmShadow agent activity crossed an organizational boundary
Beam guides AI agents in their own context instead of only allowing or blocking. How Monitor, Guide, Confirm and Enforce policies work across platforms.
OWASP’s Q3 exploit roundup says prompt-level instructions alone do not establish a secure boundary. There is a considerable difference between the limits we describe to a model and the limits its operating environment actually enforces.
Hanah Darley
Field note · 002SEEN IN THE FIELD
Large consumer marketplace | Workforce coding agents
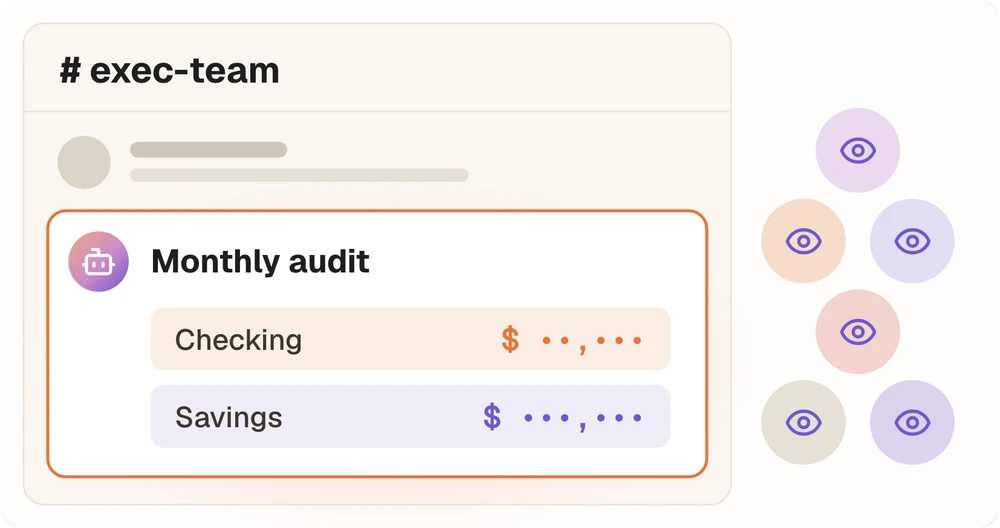
One personal agent posted a user's private financial audit into his company's exec Slack channel. Another ran 155 traces and used more than 300,000 tokens without a single prompt. We look at what GrokBot and OpenAI's Dots did on their own, and what security teams need to see as it happens.
With agents our industry has a chain-of-custody problem. Until a record leaves the agent’s control, the custodian of the evidence is the same agent being investigated.
Shane Mac’s account of an agent posting his bank balances into his company’s executive Slack channel is worth reading closely. It describes a failure pattern that will recur as agents share context, tools, and outputs.
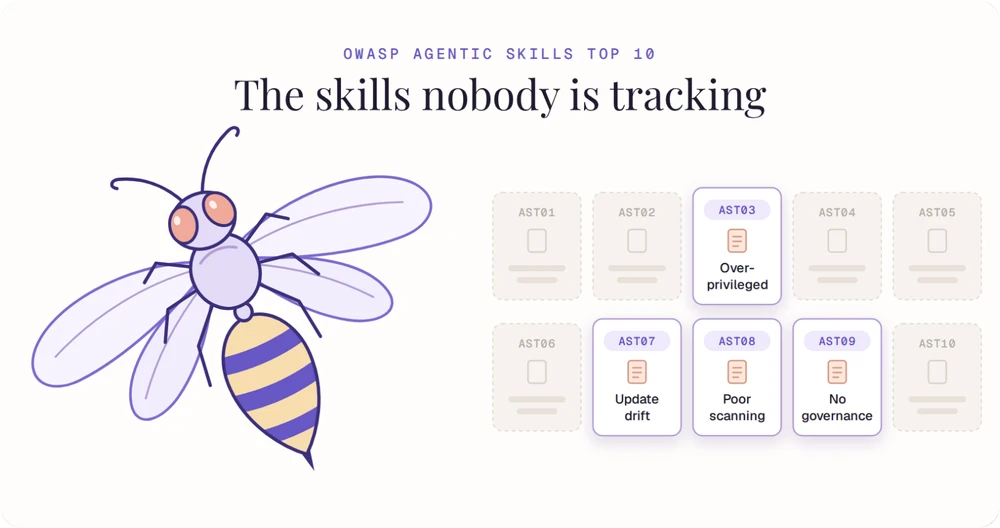
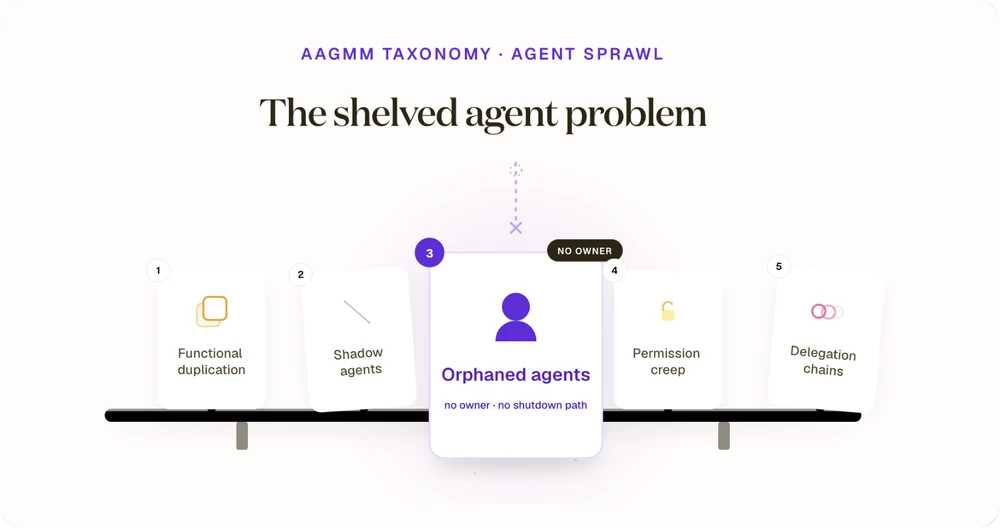
OWASP’s new Agentic Skills Top 10 gives security teams a shared vocabulary for agent skills. Most of its checks assume you already know what’s installed. Here's our read on the four risks to prioritize which unlock all the others - and why these can only be realized through a true behavioral understanding of your agents
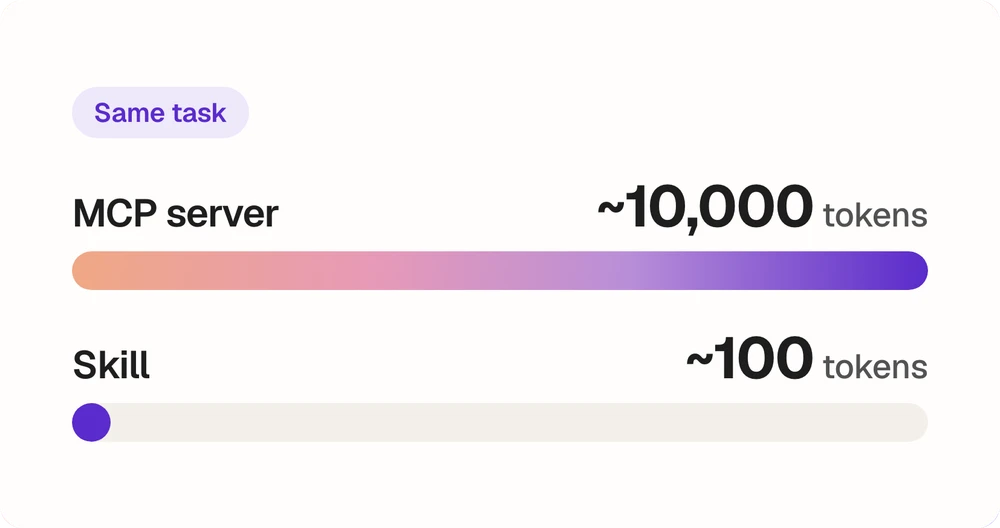
The same agent capability can cost ~10,000 tokens as an MCP server or ~100 as a skill. What that gap costs at scale - and why it's a governance signal.
A malicious skill called Clawsights ran a shell command before Claude Code's model ever reasoned about it. Refusal training was never in a position to stop it – here's the mechanism, and what to check instead.
A new academic paper shows AI agents can be compromised without a single malicious instruction, just by corrupting what the agent trusts. Here's how the attack works, why most current defenses miss it, and where security teams should focus instead.
Prompt injection gets most of the attention in AI agent security. The real risk sits in how agents behave across systems, tools, and context over time.
A remote code execution vulnerability in Claude Desktop Extensions received a CVSS 10.0 score this week. Looking at the technical requirements for exploitation reveals something more nuanced - and more instructive for agentic AI governance.
Guardrails are often treated as a universal safety layer for AI agents, but they're not. This piece explains what guardrails actually control, why they behave differently across coding agents, SaaS integrations, and custom-built systems, and how they differ from the runtime agentic remediations that sit alongside them.
The autonomous nature of AI agents requires purpose-built agentic AI governance platforms. These complement MCP gateway infrastructure with behavioral observability, contextual risk assessment, and dynamic intervention capabilities.
AI Agents aren’t just software. They make decisions that can reshape your business. Left unchecked, that power creates new forms of risk. This guide helps executives cut through the hype and focus on visibility, governance, and accountability.
Building on research from Berkeley, this article outlines five barriers to enterprise AI adoption and the AI governance best practices to overcome them with visibility and accountability.
Building AI Agents promises speed and scale, but developers know the pitfalls. Explore their insights on risks, friction points, and the steps leaders can take to enable safe, resilient adoption.
Enterprises are experimenting with AI agents, but scaling safely requires enterprise AI governance. This guide outlines how to move AI adoption from experimentation to enterprise-wide deployment with clarity, governance, and trust.
APIs, MCPs, and A2A form the foundation of AI Agent systems, yet their roles are often fragmented. This article explains how they connect, align, and collaborate, giving leaders the clarity to evaluate, govern, and scale AI adoption with confidence.
AI adoption is accelerating, but trust and accountability are essential. Learn how explainability, observability, and behavioral oversight help security teams meet regulations, manage risk, and scale AI Agents with confidence.
ACE moves enterprise AI governance beyond static prompts to living playbooks. This research note explains the model, why prompts don't scale, and where enterprises can apply it today.
Endpoint controls like EDR and XDR remain critical to enterprise defense, but they weren’t built for AI Agents. As these systems operate beyond traditional endpoints, leaders need new approaches to gain visibility, reduce risk, and extend security with confidence.
AI adoption is accelerating, but not every investment is safe. Risk mapping gives security and business leaders visibility to evaluate AI tools, weigh business impact against exposure, and make confident, accountable decisions that balance innovation with resilience.
As AI Agents evolve into autonomous actors, securing them requires techniques beyond identity and access controls. This article explores how taint analysis can extend visibility into agent workflows, uncover hidden risks, and strengthen enterprise AI security.
AI Agents can’t be black boxes. Leaders need clear visibility into how they operate to manage risk, meet compliance, and enable safe innovation across the enterprise.
Hanah Darley
Nothing matches that yet. Try another topic or a shorter search.
Elsewhere in Resources
Our definitions and gated deep dives live next door
Field guides and long-form reports, free to download.
Download →
We use analytics cookies to understand how our site is used, and you can switch them off in Preferences. With your permission, we’d also like to use marketing cookies to measure our advertising and recognize the companies that visit us. By clicking “Accept all”, you agree to marketing cookies as well. View our Privacy Policy for more information.
We use analytics and marketing cookies to understand how our site is used, measure our advertising and recognize the companies that visit us. These cookies are already on. To switch them off, click “Deny all”, or choose which to keep in Preferences. View our Privacy Policy for more information.
By clicking “Accept All Cookies”, you agree to the storing of cookies on your device to enhance site navigation, analyze site usage, and assist in our marketing efforts. View our Privacy Policy for more information.