Deep Research Discovery & Posture
A Guide to Agent Control
Geordie’s Field Guide shows the control points Anthropic, OpenAI, AWS, and Microsoft have built in natively – and where each falls short.
Geordie’s Field Guide shows the control points Anthropic, OpenAI, AWS, and Microsoft have built in natively – and where each falls short.
New capability gives AI Ops teams a clearer picture of the financial risk behind agent activity.
Henry Comfort, CEO and co-founder of Geordie AI, on raising a $30M Series A and what it means for enterprises racing to govern autonomous AI agents.
By Topic
By Content Type
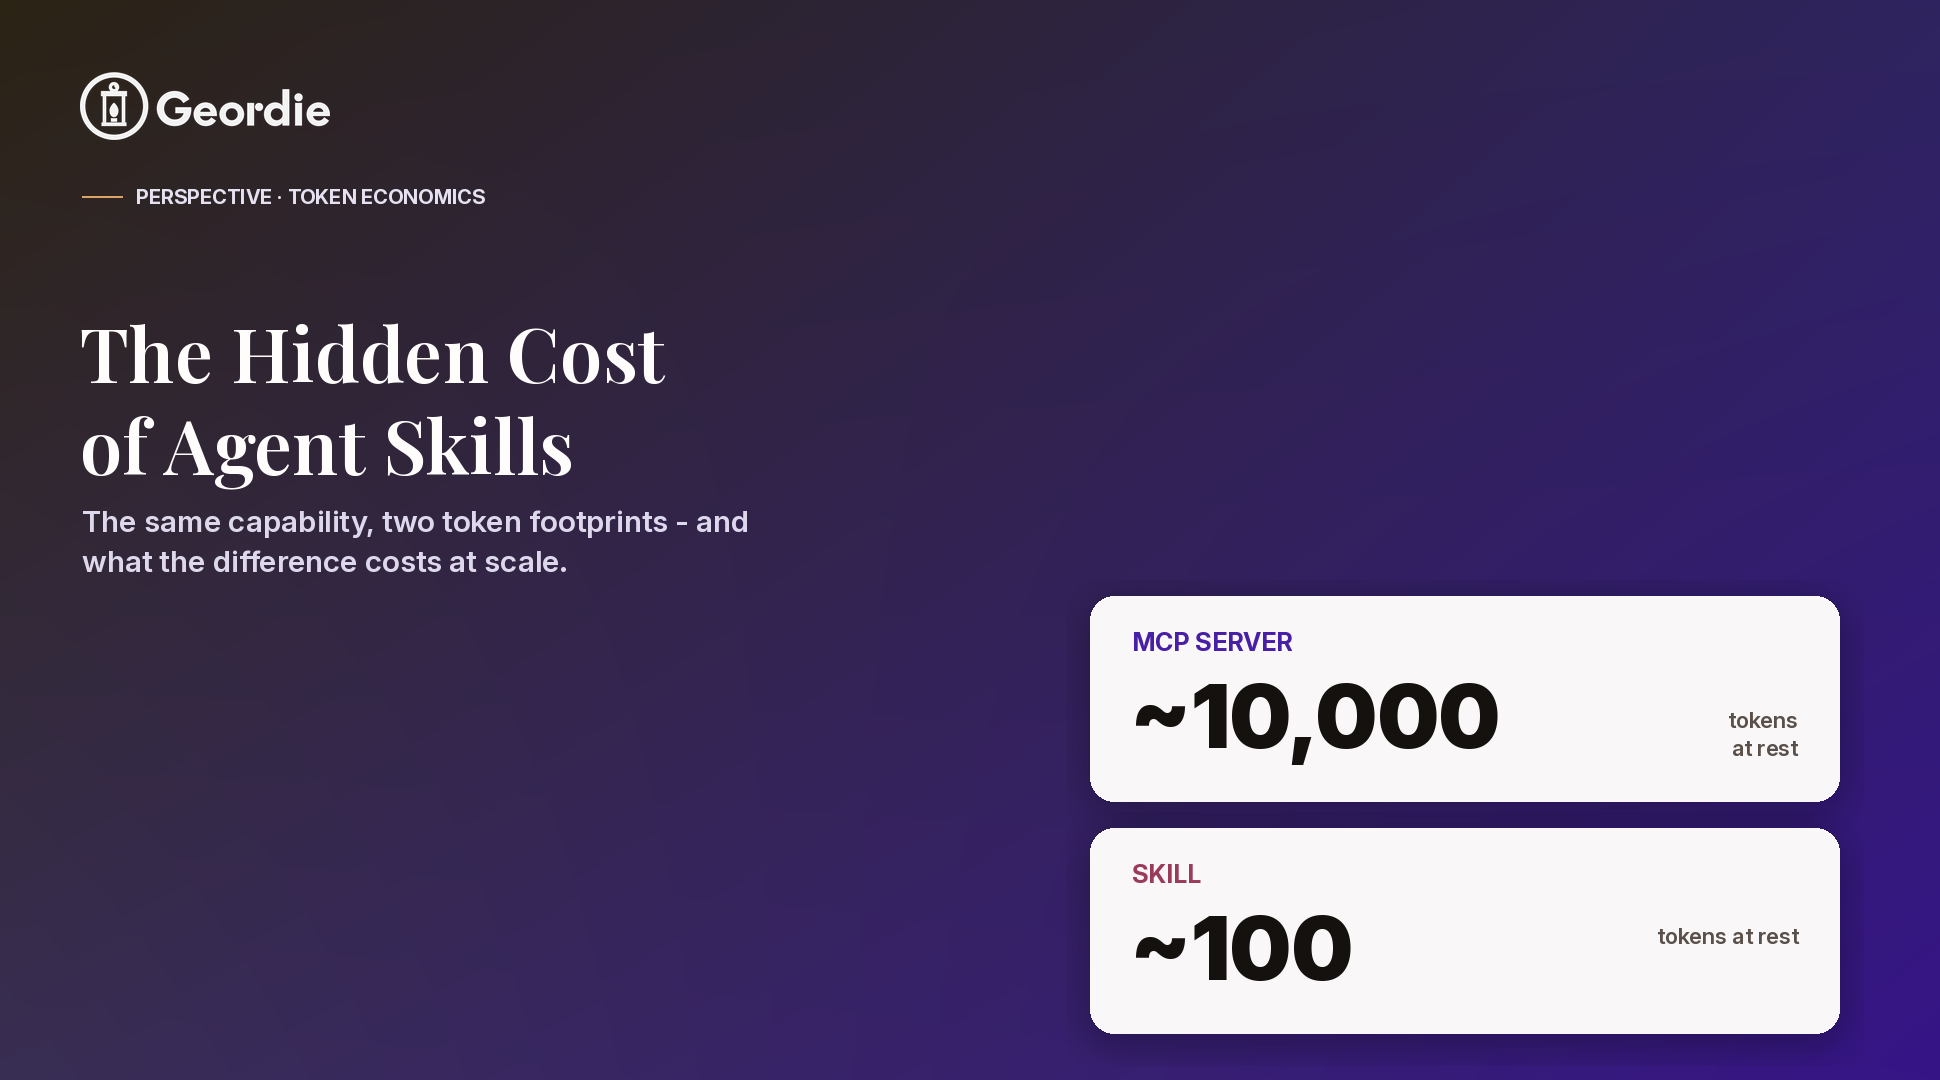
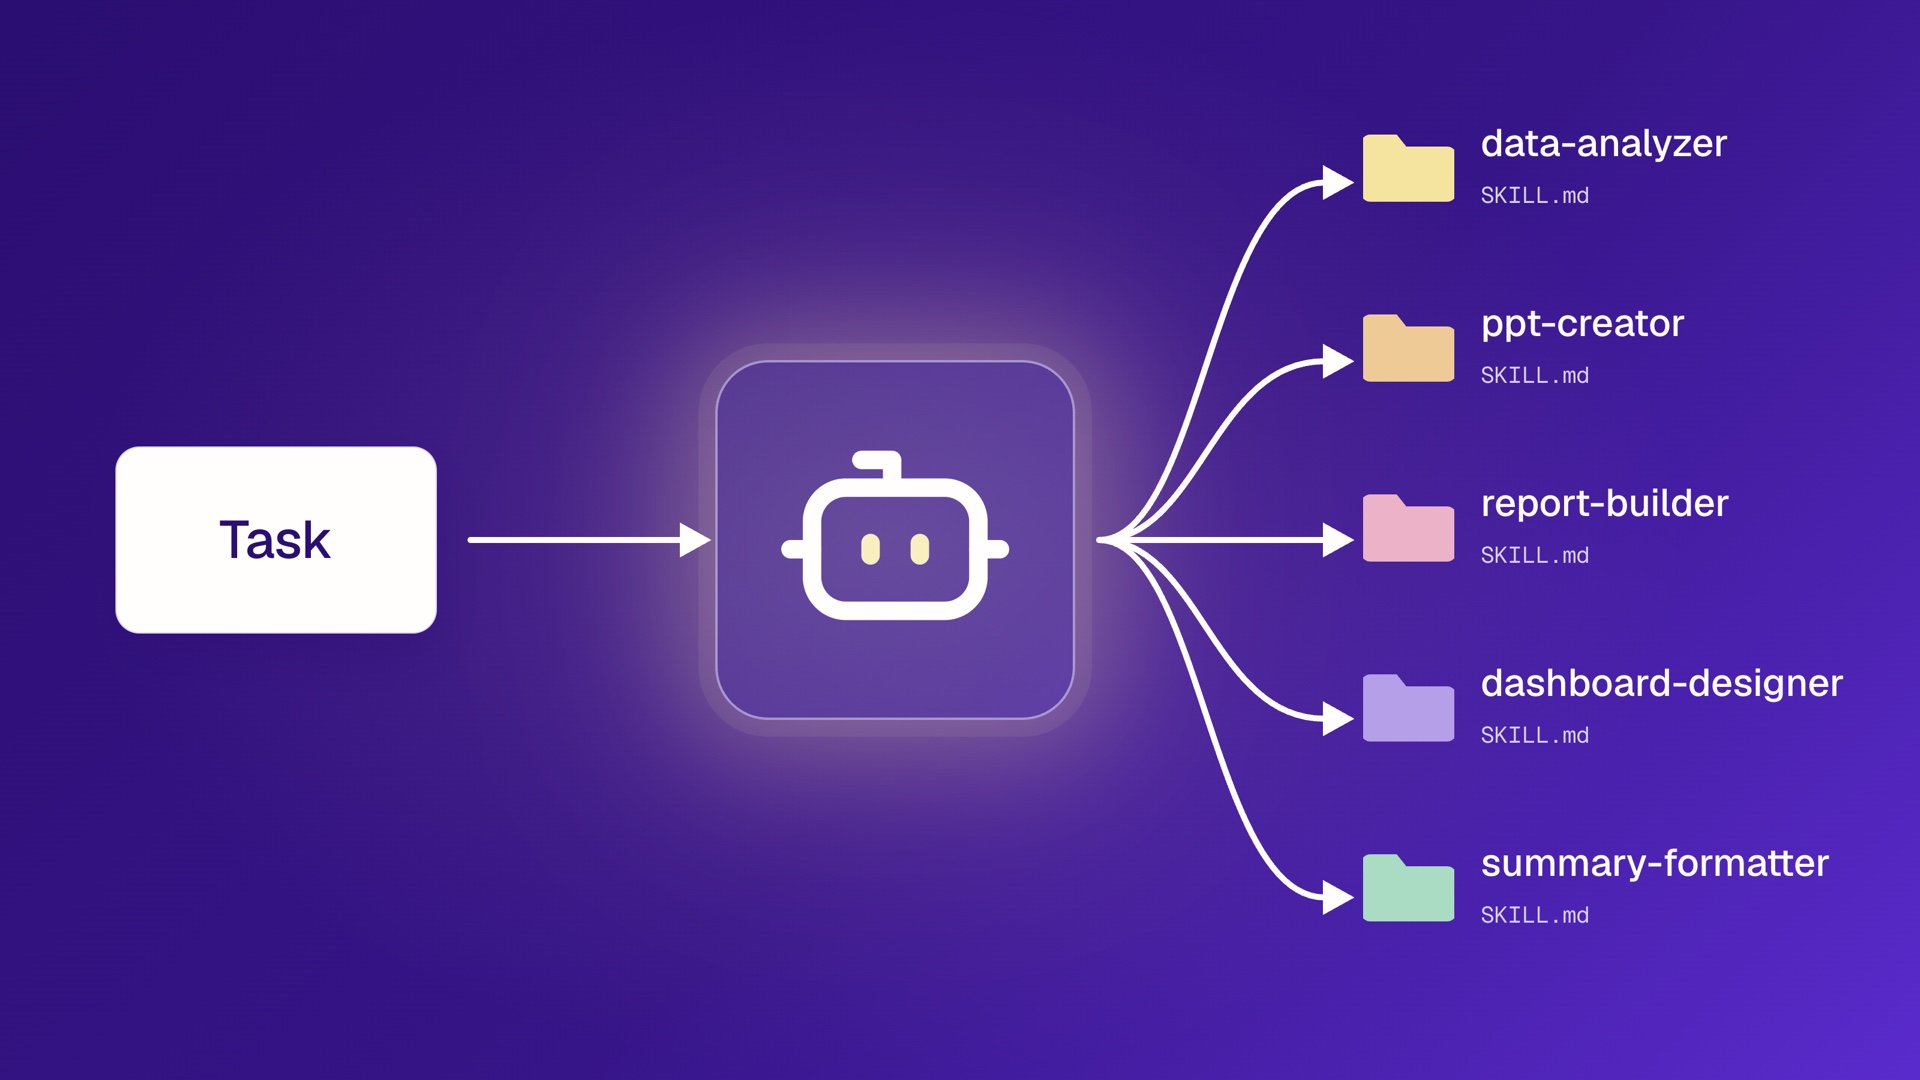
The same agent capability can cost ~10,000 tokens as an MCP server or ~100 as a skill.
Agents gain capabilities through MCP servers, skills, plugins, extensions, packages and SaaS connectors.
An AI agent audit trail is a durable record of what an agent did, under whose credentials, and in what context.
An MCP gateway sits between agents and MCP servers, applying policy to the traffic that passes through it.
Pre-approved agent template libraries optimize for control over a static asset, when the thing they're trying to control isn't static at all.
How organizations attribute, predict, and control what autonomous agents spend — and why cost and security are the same instrumentation problem.
The continuous practice of connecting what an agent is configured to do, what it can actually reach, and what it's actually doing — and how that differs from identity governance and point-in-time AI-SPM scans.
Exactly what EDR covers for AI agents, what it structurally can't, and where agent security sits alongside the controls already deployed.
What AIDR means, how it differs from AI-SPM and guardrails, and the question that separates real AIDR from monitoring with a new name.
What shadow AI is, how it differs from agent sprawl, why surveys and gateways miss it, and how detection actually works.
Move from uncertainty to informed confidence on both risk and spend, with cross-platform spend aggregation and token-efficiency mapping.

New capability gives AI Ops teams a clearer picture of the financial risk behind agent activity.
A malicious skill called Clawsights ran a shell command before Claude Code's model ever reasoned about it.
What actually turns a model into an agent — and why security controls have to target that layer, not the model itself.
Where hooks sit in an agent's execution, what they can and can't protect against, and how they compare across major platforms.
A working model for where agent skills actually create risk — and six practices for folding them into the governance you already run.
MCP servers and agent skills solve different problems and are often confused as competing standards.
Geordie’s Field Guide shows the control points Anthropic, OpenAI, AWS, and Microsoft have built in natively – and where each falls short.
A new academic paper shows AI agents can be compromised without a single malicious instruction, just by corrupting what the agent trusts.
Four disclosures in three weeks, each one showing something new, all pointing to the same governance requirements.
What is new and what MCP 2.0 means for security teams
What this incident shows about governing AI agents
New collaboration gives GuidePoint customers access to purpose-built AI agent security and governance
Meet with the Geordie team at Black Hat USA 2026 in Las Vegas, August 1–6
The company’s unique approach to securing and governing AI agents drives 50× ARR growth in the first six months of 2026
How to adopt Cowork quicker using built-in configurations alongside contextual visibility and controls
Matching security and governance to teams moving fast on AI agent deployments.
Three foundational principles for governing the agentic toolset
A practical view of agent security from our work on OWASP's latest guidance.
Helping customers keep agent controls consistent as their infrastructure evolves.
AI agent security company sees 1300% ARR growth in the first five months of the year as global enterprises adopt at scale
Henry Comfort, CEO and co-founder of Geordie AI, on raising a $30M Series A and what it means for enterprises racing to govern autonomous AI agents.
Geordie is recognized for its achievements in Security and Governance for AI Agents
Geordie announces integration with Claude Compliance API to extend security and governance across the Claude Enterprise deployment surface
Go beyond identity to a broader maturity model of prompts, guardrails and behavior
Two Critical RCE flaws and five High-severity vulnerabilities in n8n, exploitable by any authenticated user.
Proactive security controls allow forward-looking teams to secure AI agents at scale
Prompt injection gets most of the attention in AI agent security.
A threat actor compromised the Trivy vulnerability scanner and used stolen CI/CD secrets to cascade into Checkmarx, LiteLLM, and 50+ npm packages.
Meet with the Geordie AI team at RSAC 2026 in San Francisco
Recognized for pioneering technology that enables enterprises to safely scale AI agents
An executive-level introduction to agentic security and governance, designed to help CISOs understand emerging AI agent risks and prepare for adoption.
Security researchers disclosed a tool chaining vulnerability in Claude Desktop Extensions rated CVSS 10/10, but this represents a known risk class in agentic AI systems – not a novel attack.
Authenticated attackers can escape n8n's Pyodide Python sandbox to execute arbitrary system commands with host privileges.
Critical unauthenticated remote code execution vulnerability in n8n workflow automation allows attackers to exploit content-type confusion in Form webhook file upload processing to read arbitrary files, steal credentials, and execute arbitrary code on the server.
Authenticated attackers can escape n8n's Pyodide Python sandbox to execute arbitrary system commands with host privileges.
Critical vulnerability in n8n workflow automation allows authenticated attackers to achieve remote code execution through Git node exploitation
Critical remote code execution vulnerability in n8n workflow automation platform allows authenticated users to execute arbitrary code on the server through specially crafted workflow expressions that escape the sandbox isolation.
A remote code execution vulnerability in Claude Desktop Extensions received a CVSS 10.0 score this week.
Guardrails are often treated as a universal safety layer for AI agents, but they're not.
Geordie AI selected for monitoring and governing AI agents in real time.
The autonomous nature of AI agents requires purpose-built agentic AI governance platforms.
AI Agents aren’t just software.
Building on research from Berkeley, this article outlines five barriers to enterprise AI adoption and the AI governance best practices to overcome them with visibility and accountability.
Building AI Agents promises speed and scale, but developers know the pitfalls.
Enterprises are experimenting with AI agents, but scaling safely requires enterprise AI governance.
APIs, MCPs, and A2A form the foundation of AI Agent systems, yet their roles are often fragmented.
Geordie won the Black Hat Europe 2025 Startup Spotlight.
A practical, deployment-level guide to patching recent mcp-server-git CVEs - explaining how uvx caching, pip installs, and outdated Docker images can leave systems vulnerable, and how to verify you’re actually fixed.
AI adoption is accelerating, but trust and accountability are essential.
What the next Model Context Protocol (MCP) release means for enterprise security and risk teams running AI agents in production.
ACE moves enterprise AI governance beyond static prompts to living playbooks.
Why OpenClaw matters less as a vulnerability story and more as a signal that personal autonomous agents have arrived.
Endpoint controls like EDR and XDR remain critical to enterprise defense, but they weren’t built for AI Agents.
AI adoption is accelerating, but not every investment is safe.
Eight high-to-critical n8n vulnerabilities disclosed in February 2026 invalidate earlier patching guidance.
As AI Agents evolve into autonomous actors, securing them requires techniques beyond identity and access controls.
A practical breakdown of recent n8n vulnerabilities, explaining exposure, risk, and how to choose the right remediation path.
AI Agents can’t be black boxes.
We started Geordie to build the governance layer for AI agents.
No resources match your filters.
We're exploring new ground... more coming very soon